This week, I had the opportunity to attend the Global Regulatory Compliance Summit at Microsoft headquarters in Redmond.
Spending two days on the Microsoft campus is always a great experience, but what made this event particularly valuable was the combination of interesting discussions, different perspectives, and the amount of practical information being shared.
Regulatory compliance can easily become a topic dominated by legislation, frameworks, and checklists. At the summit, however, the discussions went much further than that.
Compliance Is Becoming Part of Everything We Do
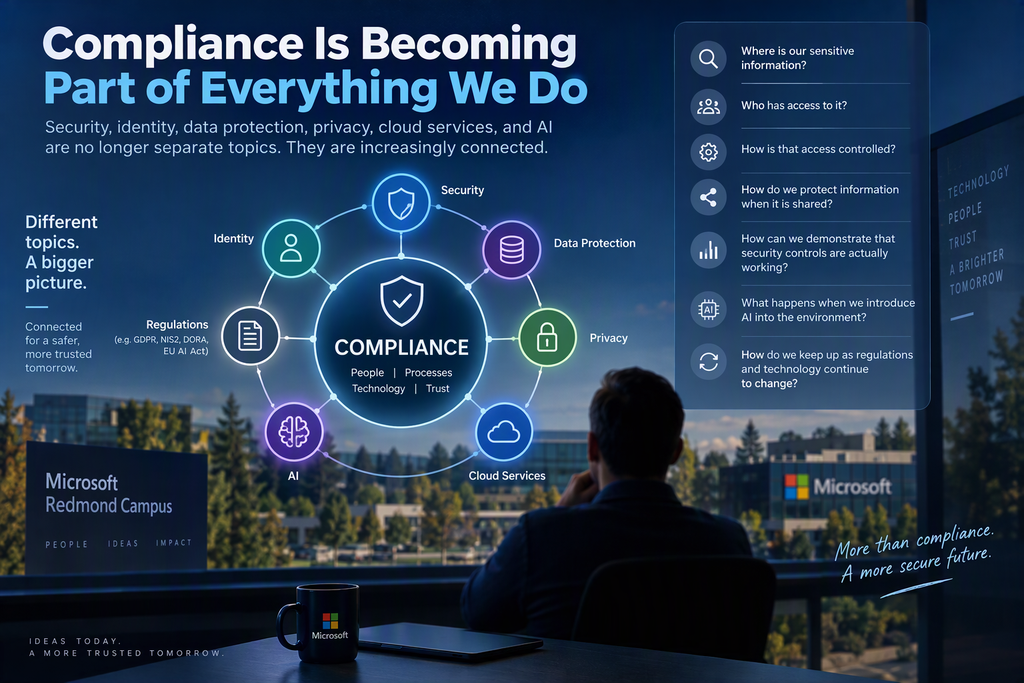
One of my biggest takeaways is just how closely compliance is becoming connected with everyday IT decisions.
Security, identity, data protection, privacy, cloud services, and AI can no longer be treated as completely separate topics. They are increasingly connected.
Organizations aren’t simply asking whether their environment is secure anymore. They also need to understand:
- Where is our sensitive information?
- Who has access to it?
- How is that access controlled?
- How do we protect information when it is shared?
- How can we demonstrate that security controls are actually working?
- What happens when we introduce AI into the environment?
- How do we keep up as regulations and technology continue to change?
These questions created some very interesting discussions throughout the summit.
Valuable Discussions Beyond the Presentations
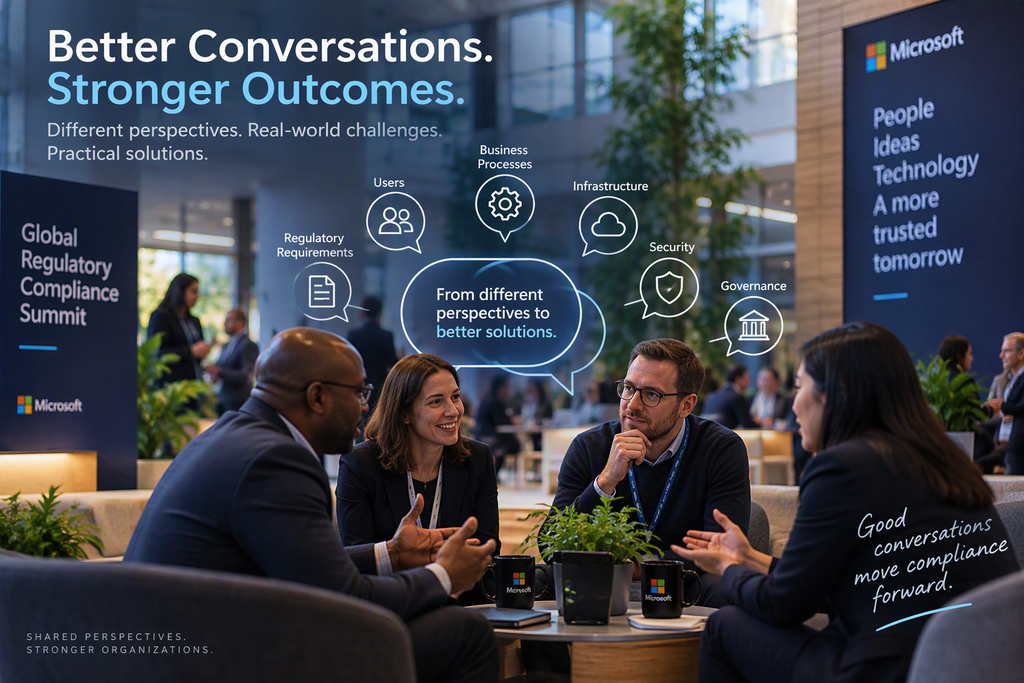
Some of the most valuable moments at an event like this aren’t necessarily the presentations themselves.
They’re the conversations that happen around them.
Being able to discuss regulatory challenges with people who approach them from different perspectives helps you look at familiar problems differently.
A technical requirement that seems straightforward on paper can become much more complicated when you consider how it affects users, business processes, existing infrastructure, security, and governance.
Those discussions help bridge the gap between what regulations require and what organizations actually need to implement.
For me, that was one of the strongest parts of the summit.
Technology Is Only Part of the Answer
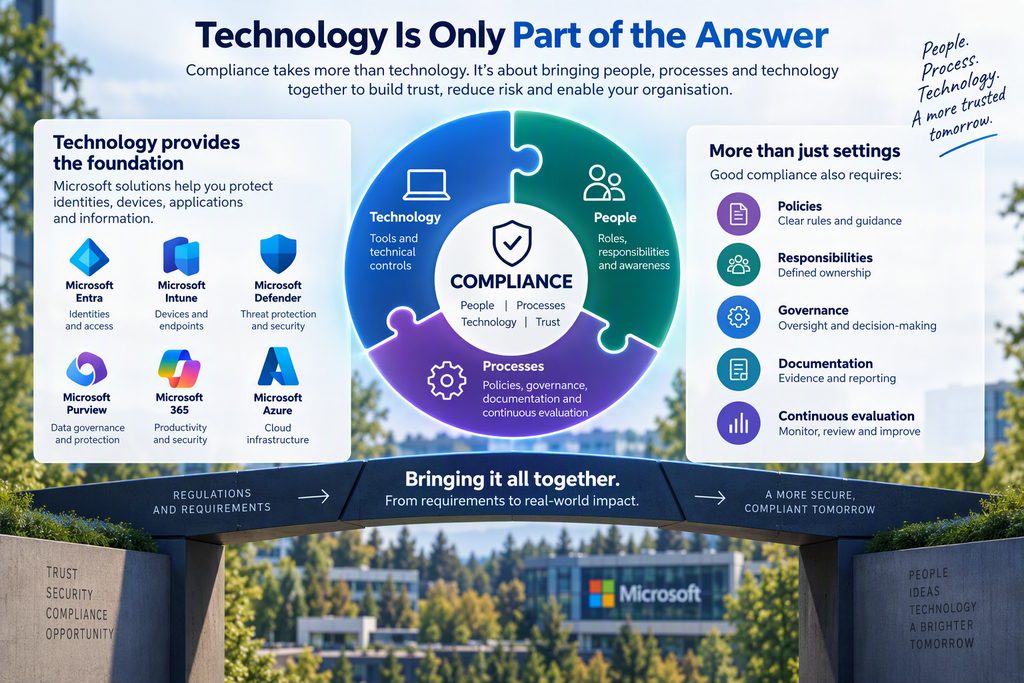
Another important point reinforced during these two days was that compliance isn’t something you solve simply by enabling a few settings.
Technology can certainly help.
Microsoft platforms such as Microsoft Entra, Microsoft Intune, Microsoft Defender, Microsoft Purview, Microsoft 365, and Azure provide many of the technical controls organizations need to protect identities, devices, applications, and information.
But technology is only one part of the picture.
Good compliance also requires clear processes, responsibilities, policies, governance, documentation, and continuous evaluation.
The real challenge is bringing all those elements together.
AI Adds a Completely New Dimension
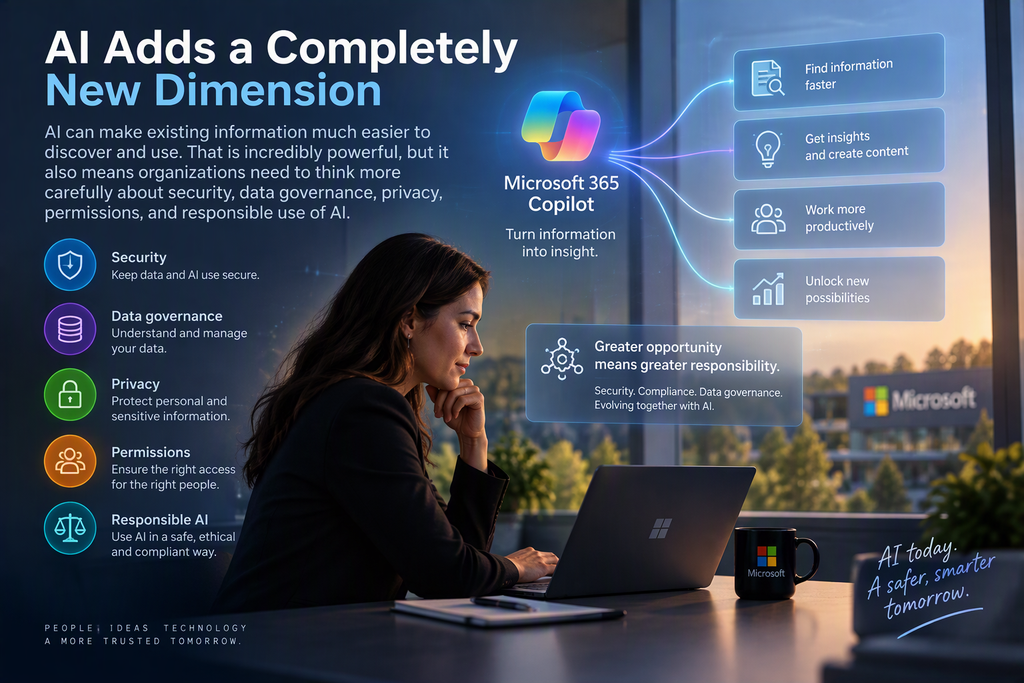
Of course, AI was also an important part of the conversations.
The rapid adoption of services such as Microsoft 365 Copilot means organizations need to think even more carefully about security, data governance, privacy, permissions, and responsible use of AI.
AI can make existing information much easier to discover and use.
That is extremely powerful, but it also means organizations need to understand their data better than ever before.
For me, this is another reason why security, compliance, and data governance shouldn’t be treated as projects that are ever truly “finished”. They need to evolve together with the technology we’re introducing.
Turning Information Into Something Practical
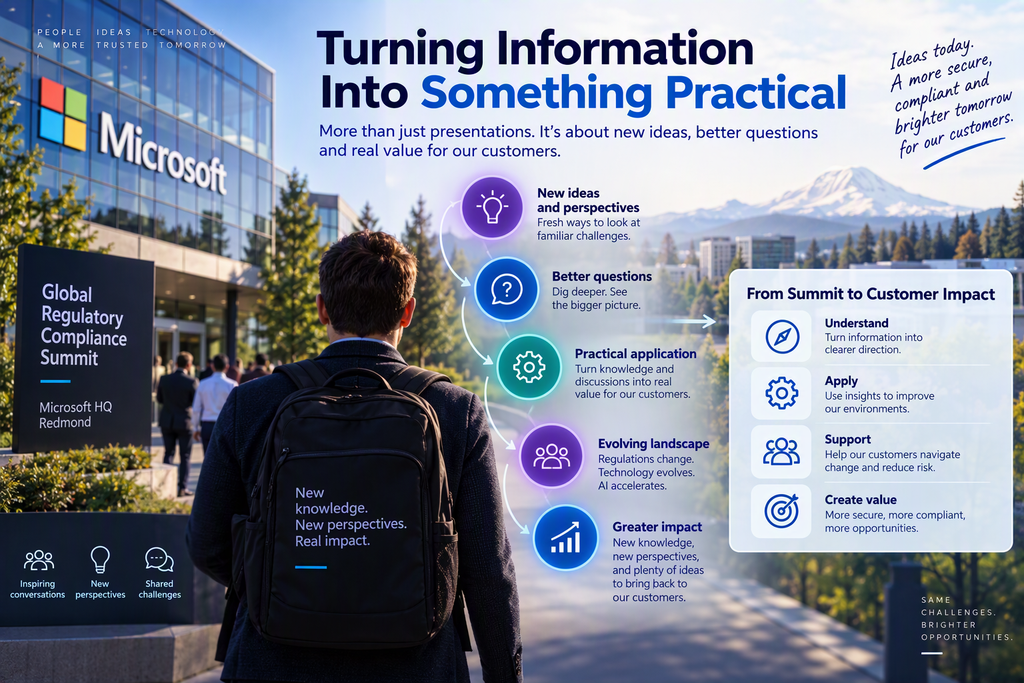
I came away from the summit with a lot of information, but more importantly, with new ideas and perspectives.
And that is where I believe the real value of attending an event like this lies.
It’s not about returning home with hundreds of presentation slides.
It’s about asking better questions.
It’s about looking differently at the environments we manage.
And it’s about taking the knowledge and discussions from those two days and turning them into something practical that can help our customers.
The regulatory landscape will continue to change. Technology will continue to evolve. AI will certainly accelerate that evolution even further.
Being able to spend two days at Microsoft HQ, exchanging ideas and learning from people who are working with these challenges every day, was incredibly valuable.
I left Redmond with new knowledge, new perspectives, and plenty of ideas to bring back to our customers.
And ultimately, that’s exactly what I hope to get from an event like the Global Regulatory Compliance Summit.